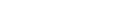
fp_live_.
Sending your key
Send your key with every request, using either of these headers:unauthorized error:
API key ≠ proxy credentials. The API key authenticates calls to
flameproxies.com/api/customer. Your package username and password authenticate proxy traffic through proxy.flameproxies.com — they’re the credentials returned by get a package and used in the lines from generate proxies. The two are managed separately and aren’t interchangeable.Getting your key
Your API key is on the API docs page of the dashboard, along with its status and your customer ID. Keys are shown only once. Copy your key and store it securely when it’s displayed — you can’t view it again later.Rotating and revoking keys
You manage your key from the same dashboard page:- Rotate key — replaces your key with a new one. Rotate any time, for example on a schedule or after someone leaves your team. Update your integrations with the new key.
- Revoke key — disables your key. Requests that use it fail with
unauthorized.
Best practices
- Store your key in a secrets manager or environment variable, never in code or client-side bundles.
- Call the API only from your backend. Never expose the key in a browser or mobile app.
- Rotate the key immediately if you suspect it has leaked.
Next steps
API quickstart
Make your first API request.
Error handling
What to do when a request fails.